Local security software · Private pilot
PRAE Platform
Run security checks from your coding assistant.
Connect your assistant to a local project through the Model Context Protocol (MCP). Choose the files it can examine, inspect each finding and verify the fix against a fresh run.
Products
MCP software · Private pilot
PRAE Platform
Run local security checks from your coding assistant and keep the evidence for each finding.
Explore the platformPublic intelligence · Free
Vigilance
Look up a vulnerability, read the affected conditions and go directly to the vendor’s guidance.
Search advisoriesDeveloper tools · Free alpha
Ship Kit
Run four offline checks against selected project files. Individual and Studio licenses are in development.
Try the alphaDigital publication · Available
Security Field Kit
Run a human-led release review with a field guide, editable workbook, control register and worked example.
Explore the Field KitImplementation playbook · In development
Access and Data Boundaries
A planned workflow for testing access between accounts, organizations and staff roles.
View the outlineSelf-paced course · In development
Security Foundations for Builders
A planned course for builders who want to practice scoping, testing and documenting security boundaries.
View the curriculum
Inside the MCP platform
What changed after the fix?
In a pilot test project, the dependency manifest and lockfile disagreed. The platform kept the original finding alongside the evidence from the corrected build.
Read the assessment example- Input
- npm manifest and lockfile
- Finding
- Direct dependency mismatch
- Verification
- Fresh assessment of the corrected files
Finding statusResolved
Digital publication
The Security Field Kit
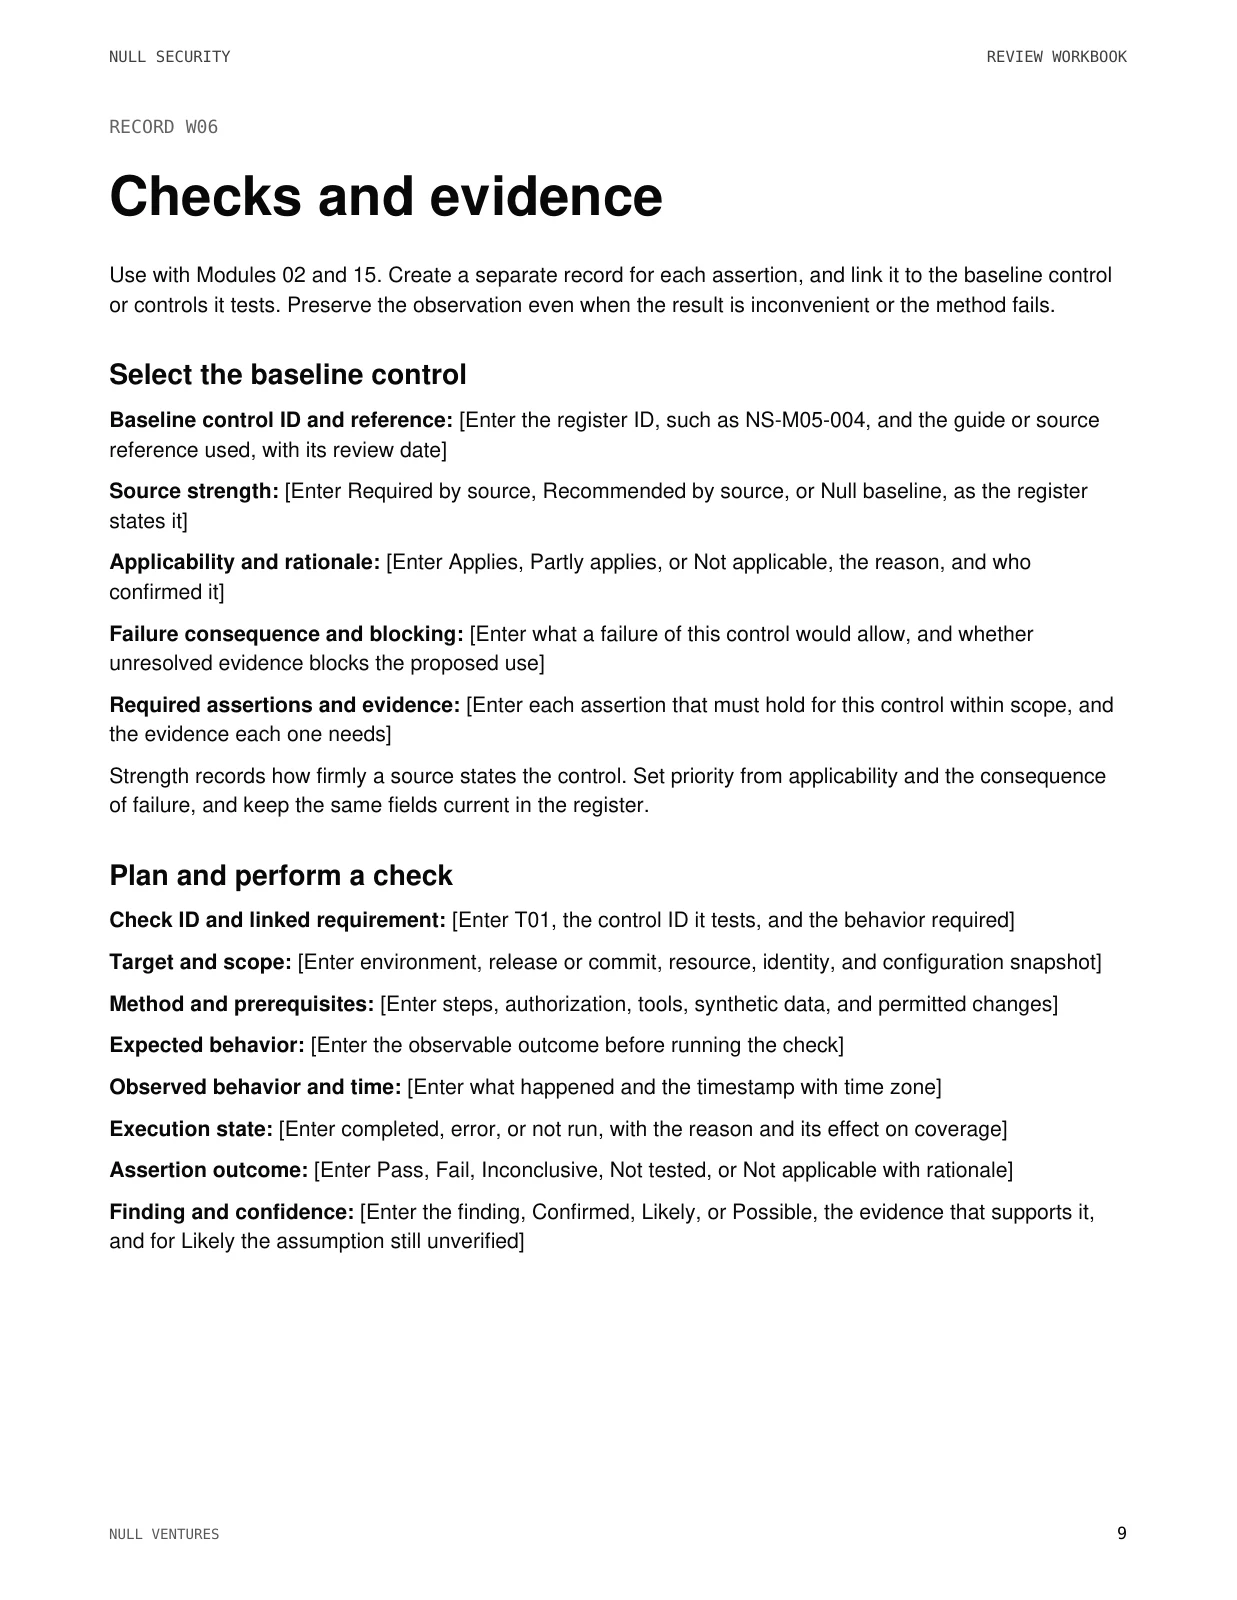
For a team running its own release review. The field guide, workbook and 244-control register give you a place to record what passed, what remains open and who owns it.
US$149 · One-time purchase · Taxes included
Free resources
Start with one system.
Define the boundary you need to protect before you work through a full review.
PRAE research
Security before implementation.
Our research asks what software must allow, what it must refuse and how teams can tell when the evidence has gone stale.
Browse the researchTrace how a public issue redirected an agent into private repositories.
Vigilance reportsCheck which systems a published vulnerability affects and what to verify locally.
Boundary Contract CompilerProposed software, in development. Read the design for turning security requirements into independent tests.